
A common misconception in DeFi is that choosing a wallet is mainly a question of storage: where private keys are kept, how attractive the interface looks, or how many networks appear in a dropdown. For active users, that is only the beginning. The harder problem is interpreting what a decentralized application is asking a wallet to do before a transaction becomes irreversible.
That distinction matters in the United States, where DeFi users may move between lending markets, decentralized exchanges, liquid staking services, bridges, and newer protocols across several EVM-compatible chains. A wallet that merely connects to these applications is useful. A wallet that helps the user understand the transaction, the destination, the assets involved, and the likely outcome addresses a much more important part of the risk.
Connection is not the same as comprehension
Decentralized applications, or dApps, are web interfaces that communicate with blockchain smart contracts. When a user clicks “swap,” “supply,” “borrow,” or “stake,” the application typically constructs a transaction. The wallet then presents that transaction for approval and broadcasts it after the user signs.
The key misconception is that the wallet controls the application. In most cases, it does not. A wallet can display, interpret, or warn about a request, but the smart contract determines what the signed transaction actually executes. This creates a useful division of responsibility: the dApp proposes an action, the wallet helps the user inspect it, and the blockchain enforces the final call.
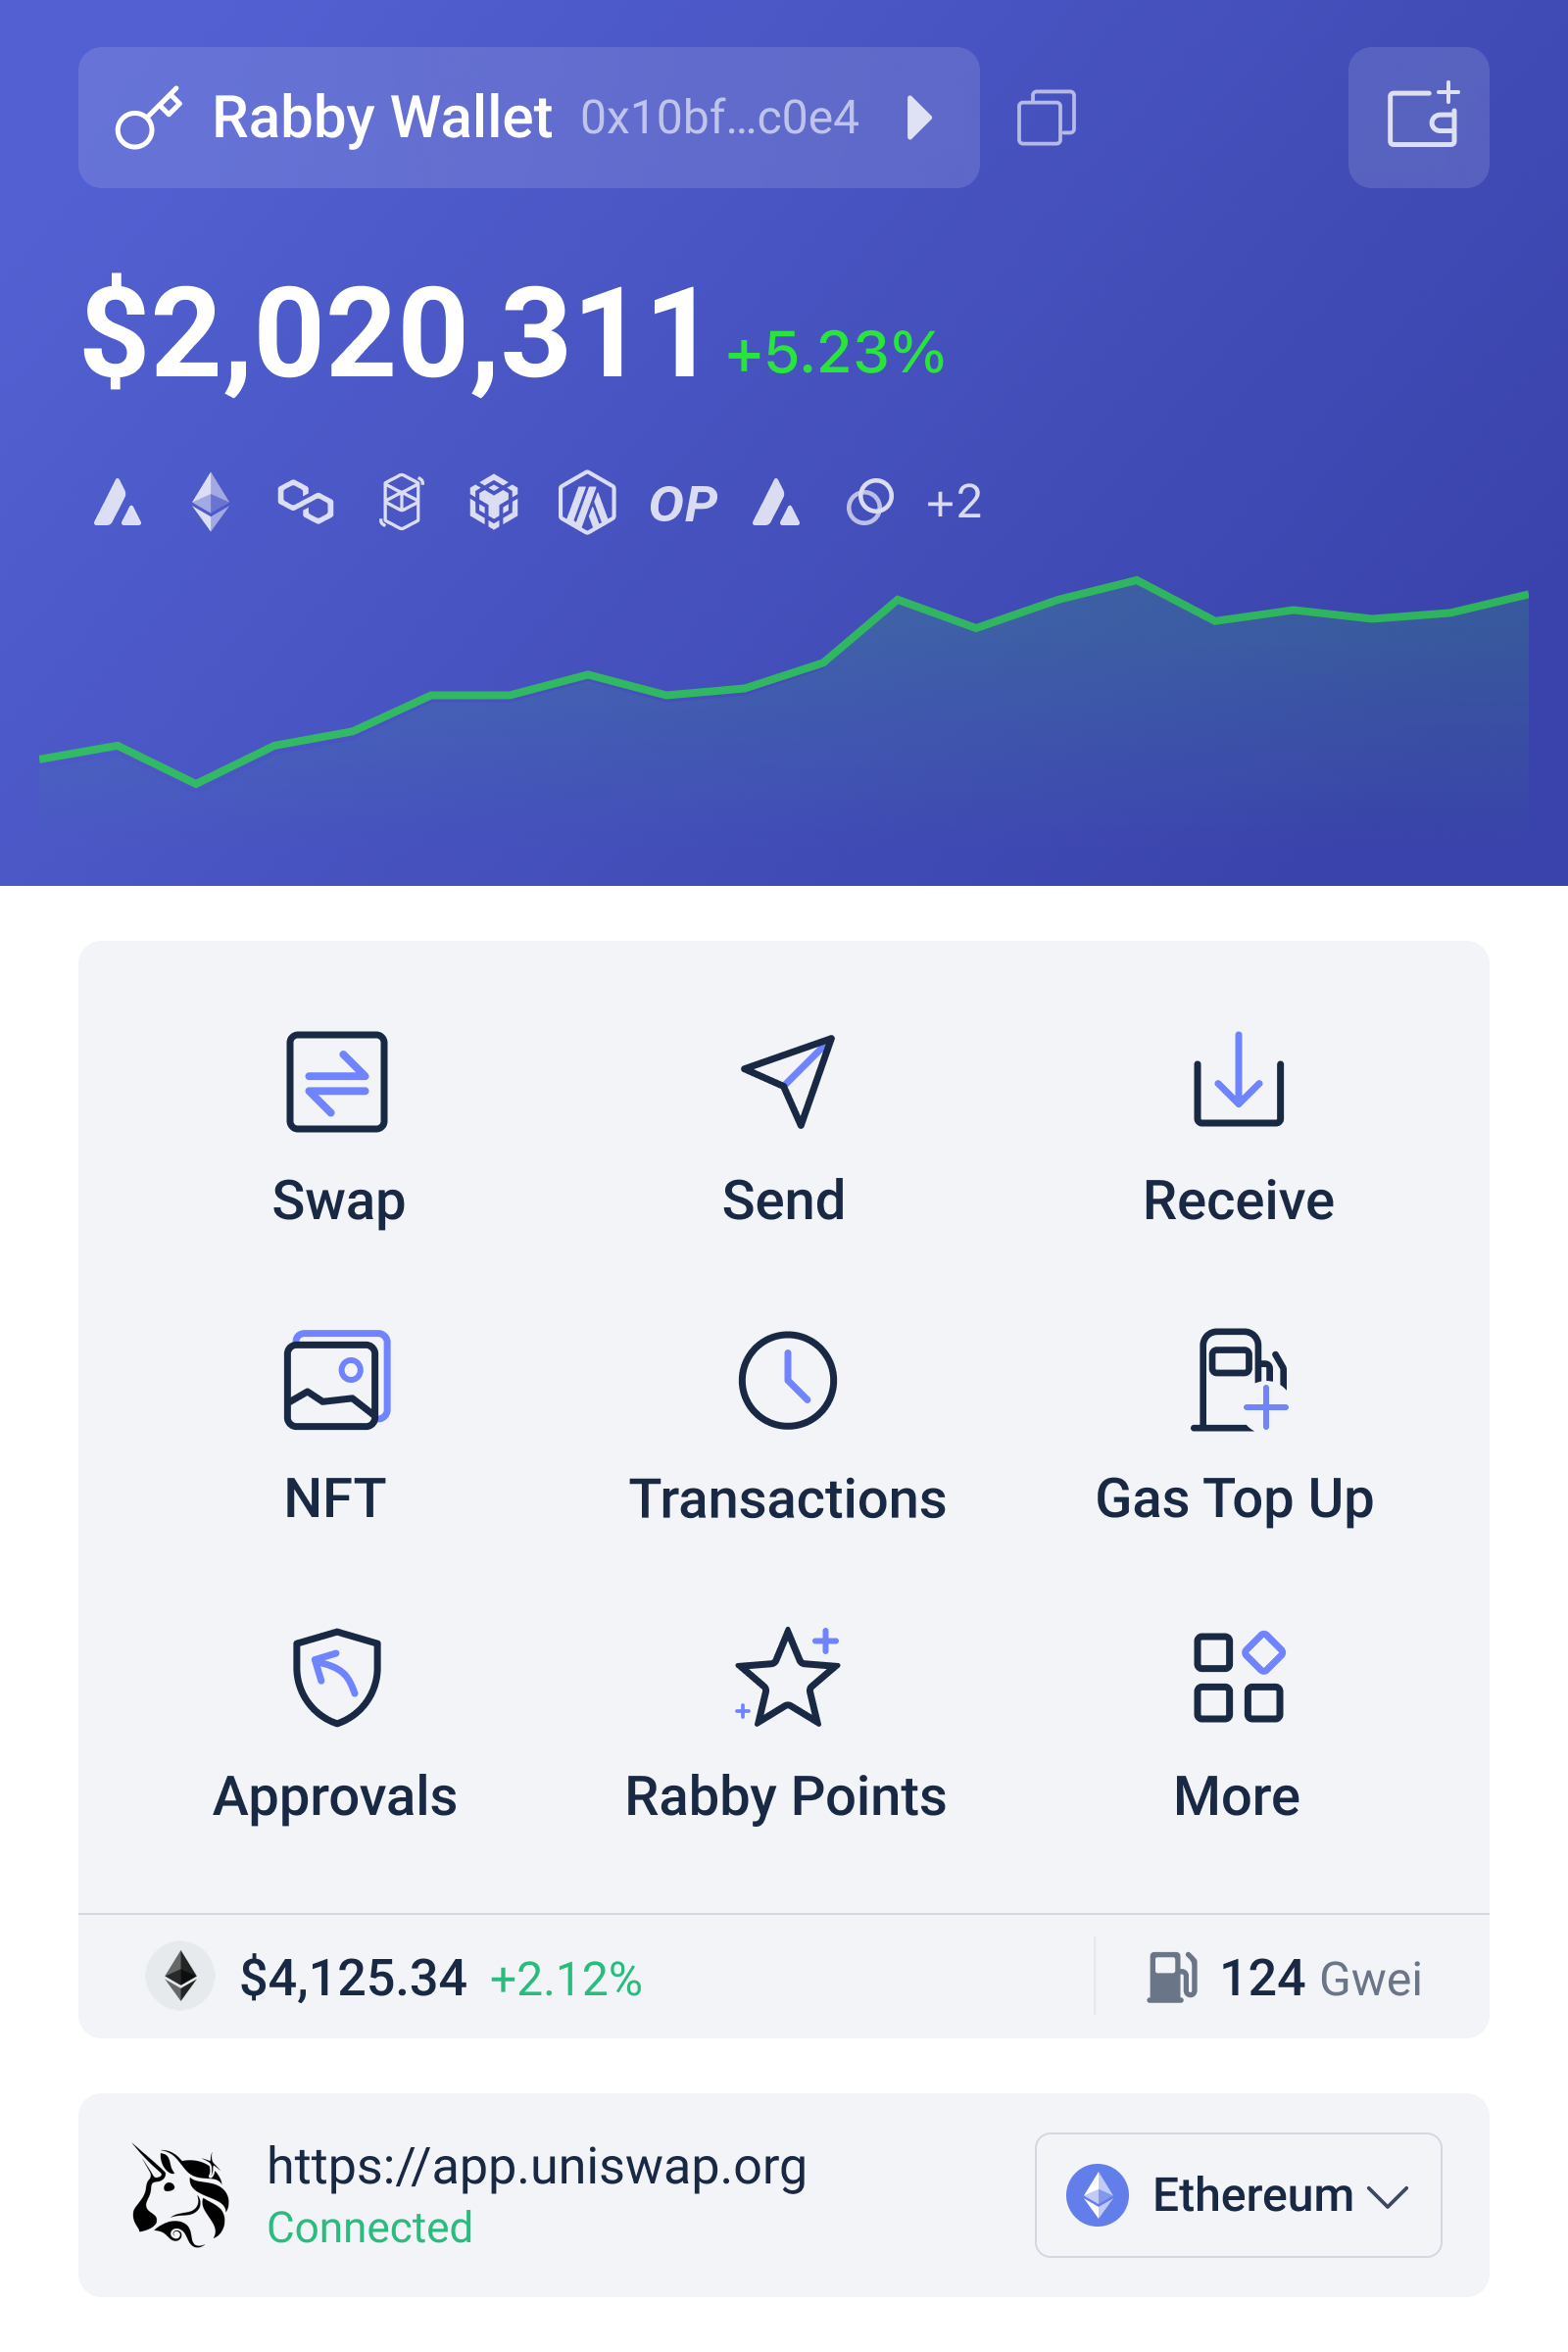
For users exploring a rabby wallet approach to DeFi, the practical value lies in making that inspection step more informative. Wallet features such as transaction simulation and security warnings are not substitutes for protocol research. They are tools for reducing avoidable mistakes before capital is exposed.
A simulation can provide an estimate of the state change that would follow from a transaction: which token balance may decrease, which asset may arrive, whether an approval is being granted, or whether a call is likely to revert. This is more useful than simply recognizing a contract address. A legitimate-looking address can still be used in an unexpected transaction, and a familiar protocol can present a poorly configured or malicious front end.
Comparing the main wallet approaches
Basic browser wallet
A conventional browser wallet is often sufficient for straightforward transfers and occasional interaction with established applications. Its strength is simplicity. Users generally understand the core sequence: connect, confirm, sign, and wait for the transaction to settle.
The limitation appears when transactions become composable. A single click may trigger several contract calls, use a token approval, route a swap through multiple pools, or interact with a protocol the user has not previously examined. In that environment, a basic confirmation window may show technical data without translating it into a useful risk decision.
Hardware wallet paired with a browser interface
A hardware wallet protects signing keys by keeping them in a separate device. That is a meaningful defense against some forms of malware and unauthorized key extraction. It is particularly relevant for larger balances or long-term holdings.
Yet hardware protection does not make a transaction safe by itself. A user can still approve a harmful contract call on a hardware device. The device may confirm that the user is signing a valid cryptographic message, while the user remains mistaken about what that message authorizes. Key isolation and transaction comprehension solve different problems.
An interpretation-focused wallet
A wallet designed around dApp activity attempts to narrow that gap by emphasizing chain compatibility, asset awareness, simulation, and warnings during the signing process. This can make a difference when a user moves quickly among EVM chains, because network selection, token identity, approvals, and contract behavior are easy to confuse.
The trade-off is cognitive rather than purely technical. More information can improve decisions, but only if the user knows what deserves attention. A warning is not automatically evidence of fraud, and the absence of a warning is not proof of safety. Detection systems can be incomplete, especially when contracts are new, upgradeable, complex, or dependent on off-chain infrastructure.
Why transaction simulation matters in DeFi
Transaction simulation is best understood as a preview, not a prophecy. The wallet attempts to estimate how a transaction would execute against available blockchain state. That can reveal an unexpected token transfer, a failed call, a changed balance, or an approval that is broader than the user intended.
This is especially valuable for DeFi because protocols are composable. A swap may involve a router contract, several liquidity pools, and token contracts. A lending action may change collateral, debt, liquidation exposure, and interest accrual. A bridge transaction may create a message that is later processed by a separate system. The user sees one button; the underlying system may perform a chain of operations.
Simulation therefore changes the question from “Do I recognize this dApp?” to “What state change is this transaction proposing?” That is a sharper mental model. Brand familiarity is a weak security signal. Expected state change is a stronger one, although it still requires context.
There are boundaries. A simulation can become stale if the blockchain state changes between preview and execution. It may not fully capture off-chain decisions, oracle updates, sequencer behavior, MEV conditions, bridge validation, or future contract upgrades. Some signatures are messages rather than ordinary transactions and may not produce an obvious balance change at signing time. Users should treat simulation as one layer in a review process, not as an oracle that guarantees the outcome.
Approvals, signatures, and the hidden surface of risk
Many DeFi losses do not begin with a user sending assets directly to an attacker. They begin with an approval. An ERC-20 approval allows a spender contract to move tokens on the user’s behalf, sometimes up to a specified amount and sometimes without a practical limit.
This creates a subtle difference between permission and payment. A user may approve a contract today and discover the consequence only later, when the spender invokes that permission. Revoking old approvals can reduce exposure, but it is not a universal solution: revocation transactions cost network fees, and revoking an approval does not repair assets already lost or protect against every type of signed authorization.
Permit-style signatures and other off-chain approvals add another layer. Because they may not immediately appear as a conventional blockchain transaction, users can underestimate their significance. A careful workflow distinguishes among a token approval, a direct transfer, a contract interaction, and a message signature. Each deserves a different question: what is being authorized, who can use it, for how long, and under what conditions?
A practical framework for comparing wallets and dApps
When evaluating a wallet for regular DeFi use, four questions are more useful than simply counting supported chains.
- Visibility: Does the wallet explain the expected assets, approvals, recipients, and contract actions in terms a user can verify?
- Context: Does it help distinguish a normal interaction from an unusual or high-risk request?
- Control: Can the user separate trading funds, long-term holdings, and experimental capital across accounts or devices?
- Recovery: What happens if a device is lost, a seed phrase is exposed, or an application is compromised?
This framework also clarifies why no single wallet is best for every user. A frequent trader may value fast dApp switching and rich previews. A long-term holder may prioritize hardware isolation and minimal signing activity. A developer or power user may accept more complexity in exchange for detailed contract visibility. The best setup can be layered: a hardware signer for substantial assets, a separate account for routine DeFi, and a small experimental balance for unfamiliar protocols.
Network support introduces another trade-off. EVM compatibility makes it easier to move among Ethereum and related chains using familiar transaction patterns, but similar interfaces can hide meaningful differences in gas markets, bridge assumptions, finality, sequencers, and liquidity. A wallet can make chain selection easier; it cannot erase the risks created by fragmented infrastructure.
What to watch as wallet integration evolves
Recent project messaging positions Rabby as an Ethereum and EVM wallet intended to make on-chain activity simple, fast, and secure across supported networks. The more important question is how such positioning translates into user behavior. If wallet interfaces increasingly surface simulations, approvals, contract identities, and chain context at the moment of signing, users may make fewer errors caused by interface ambiguity.
That outcome is conditional. Better warnings help only when they are understandable, timely, and calibrated. Too few warnings leave dangerous actions unnoticed; too many warnings create alert fatigue, encouraging users to approve everything. The signal to watch is not the number of security labels, but whether the interface helps users distinguish ordinary complexity from meaningful danger.
For DeFi participants, the near-term implication is practical: treat the wallet as an analytical checkpoint between an application’s request and the blockchain’s execution. Read the simulated result, inspect approvals, verify the chain, question unexpected recipients, and keep exposure proportional to how well the protocol is understood. These habits remain necessary even when the wallet’s interface is excellent.
Frequently asked questions
Does transaction simulation guarantee that a DeFi transaction is safe?
No. Simulation can reveal likely state changes and execution failures, but it may not capture every off-chain dependency, timing change, oracle event, upgrade, or bridge-related risk. It is a decision aid, not a guarantee.
Is a hardware wallet enough for secure dApp use?
A hardware wallet offers strong protection for signing keys, but it does not determine whether a signed transaction is sensible. Users can still approve a malicious contract or an excessive token allowance. Key security and transaction understanding should be treated as separate layers.
Should DeFi users revoke every token approval?
Not necessarily. Revoking unused or unnecessarily broad approvals can reduce exposure, but each revocation costs a network fee and may disrupt intended protocol use. Review approvals according to asset value, protocol trust, allowance scope, and how often the account interacts with the application.
What is the most useful wallet-selection question?
Ask whether the wallet helps you verify the transaction’s expected outcome before signing. Chain count and interface speed matter, but visibility into approvals, recipients, contract actions, and simulated balance changes is often more decision-useful for active DeFi users.
The central comparison is therefore not simply one wallet versus another. It is blind signing versus informed signing. A capable wallet can improve the second process by making complex dApp requests easier to inspect, while still leaving protocol risk, user judgment, and operational discipline in the picture. In DeFi, security is rarely a single feature. It is the quality of the decisions made before the signature becomes permanent.
